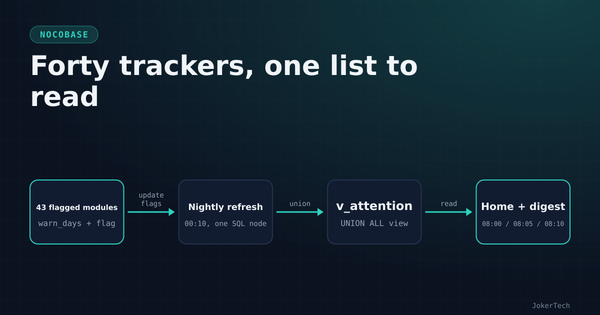
self-hosting One SQL view that tells me what is overdue across forty-odd trackers How a single UNION ALL view in NocoBase became the only list I read each morning, and the two things Postgres and NocoBase refused along the way.
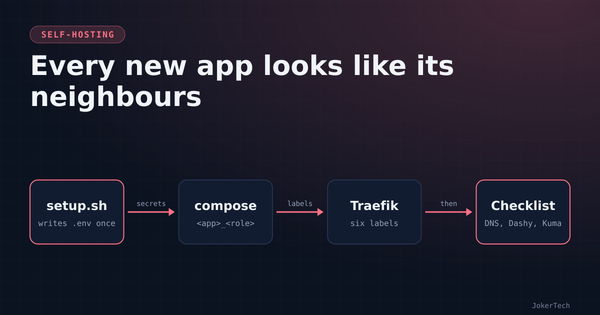
self-hosting The house rules for adding one more app to a crowded VPS One folder, one compose file, a .env.example, a setup.sh that writes the secrets, and nothing in git that the server owns. The conventions I add apps by, and where each one came from.
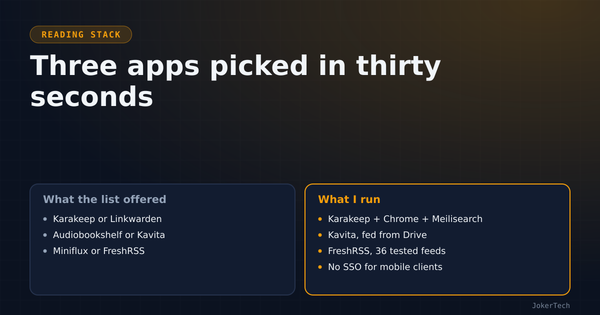
self-hosting Bookmarks, feeds and books on one VPS, and how little I compared Why my reading stack is Karakeep, FreshRSS and Kavita, what the choice really rested on, and the parts I still haven't tested.
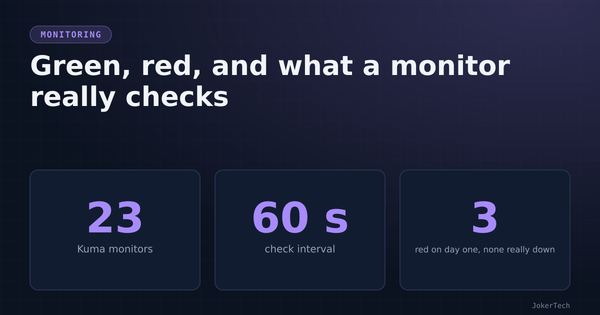
self-hosting Uptime Kuma on a single VPS: 23 monitors, three red, and why How I set up Uptime Kuma for a one-box self-hosted stack, which endpoints I point it at, how alerts reach my phone, why three monitors went red without anything being down, and the DNS app I kept off the box.
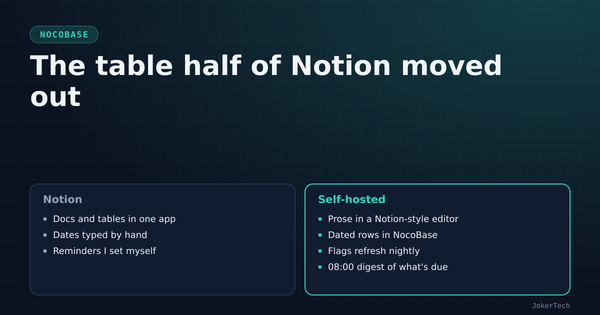
self-hosting I asked for a Notion clone and ended up living in NocoBase Why the database half of my Notion habit moved to a self-hosted NocoBase instead of a Notion look-alike, and what a day of building on it actually produced.
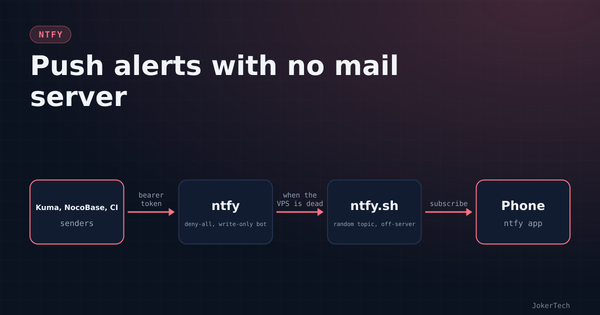
self-hosting I wanted my phone to buzz without running a mail server, so I picked ntfy Why ntfy beat Gotify, Pushover, Telegram and e-mail on my single VPS, how its users and tokens live in a .env file, and how alerts still arrive when the VPS is dead.
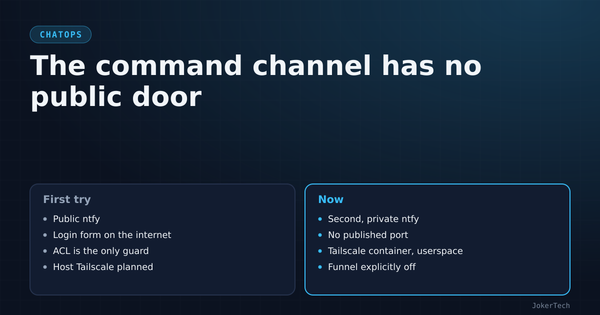
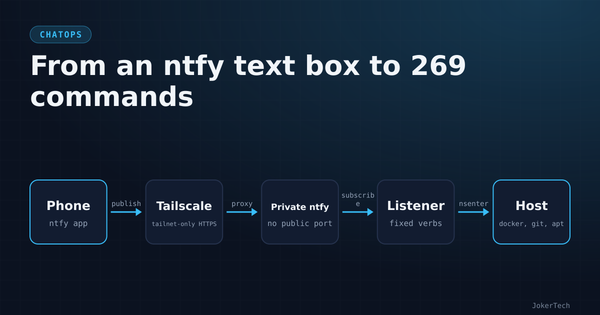
self-hosting A command channel nobody on the internet can reach: Tailscale in a container in front of a private ntfy Why my ChatOps commands go through a second, private ntfy with no public port, published to my tailnet only by a Tailscale container with Funnel switched off, and how the setup script gets there without me typing a hostname.
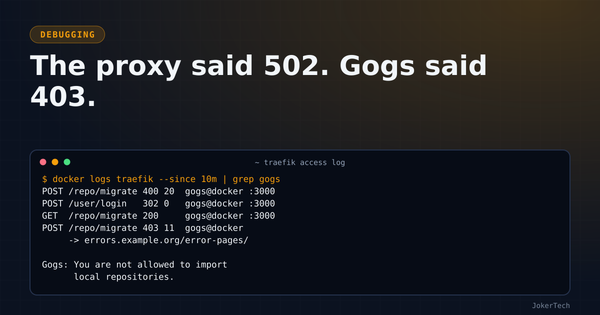
self-hosting The Bad Gateway that was really Gogs saying no Adding a GitHub mirror to Gogs kept failing with Bad Gateway. It took an hour, an SSH-key detour and a Traefik access log to find a plain 403 underneath.
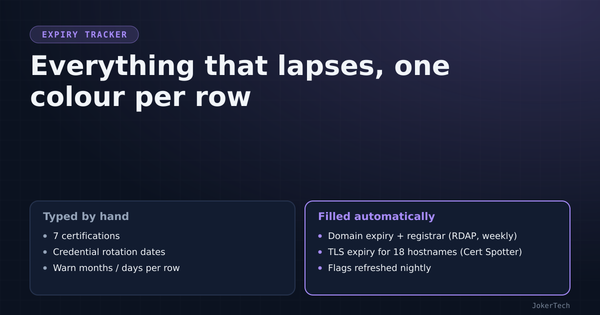
self-hosting The certificate tracker that started all this, and the API key it had to watch Professional certifications, domains, TLS certificates and API keys in one NocoBase expiry tracker, filled from RDAP and certificate-transparency logs, plus the test that deleted a real row.
self-hosting I asked for an open-source Notion and ended up running four notes apps The honest history of looking for a self-hosted Notion: AFFiNE, AppFlowy, SiYuan and Memos all got deployed, and the structured stuff went somewhere else entirely.
self-hosting Why I run my VPS from a chat topic on my phone instead of SSH How a question about logging expenses from my phone became a ChatOps listener on a private ntfy server: rebuilt four times in a day, then broken in four instructive ways once it met the real server.
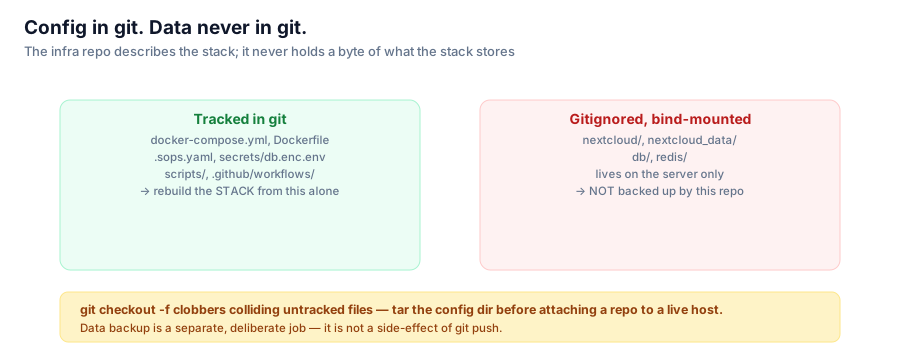
docker Why the Infra Repo Should Never Contain Your Data nextcloud/, nextcloud_data/, db/, and redis/ are bind-mounted directories that live entirely on vmi2633427, are gitignored on purpose, and are explicitly not backed up by the repo that describes the stack running on top of them.
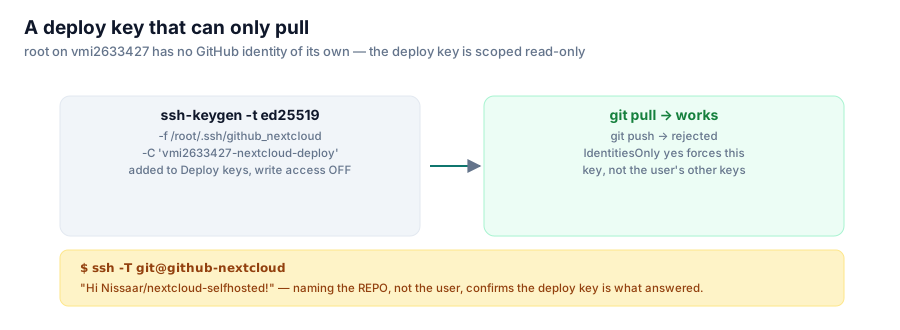
git A Deploy Key That Can Only Pull root on vmi2633427 has no GitHub identity of its own, and the deploy only ever needs to pull — so the key it authenticates with is generated, scoped, and verified to be read-only before it ever touches the server.
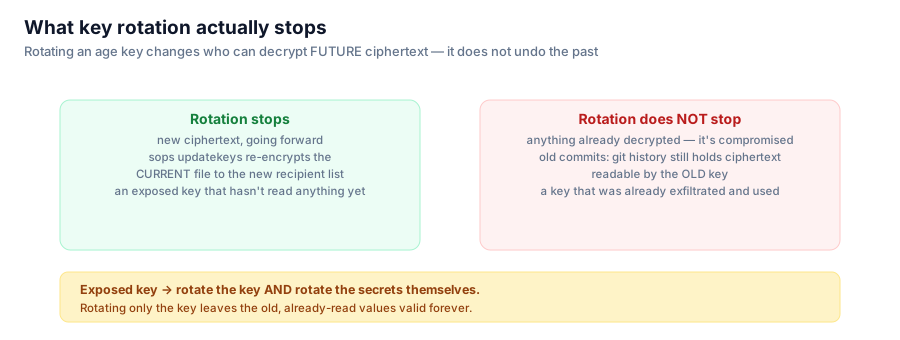
security What Key Rotation Actually Stops (and What It Doesn't) Rotating an age key re-encrypts secrets/db.enc.env to a new recipient list going forward. It does nothing to the plaintext an old key already read, and nothing to the ciphertext still sitting in earlier git commits.
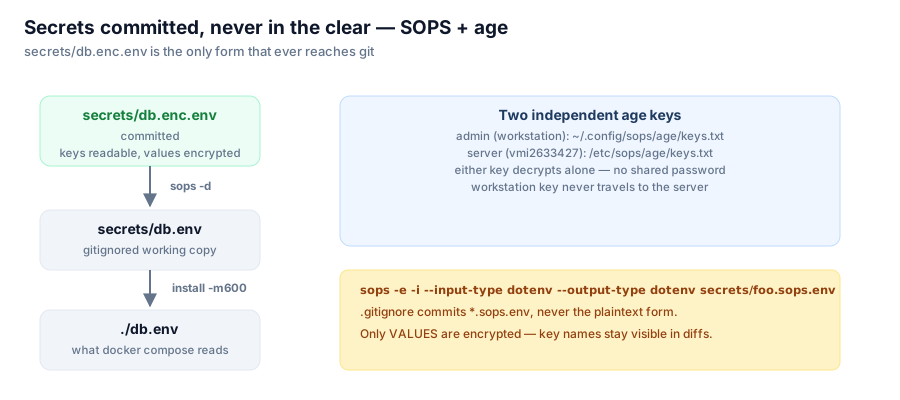
sops Keeping Secrets in a Private Git Repo Without Actually Leaking Them secrets/db.enc.env is committed to a private GitHub repo, key names visible, values encrypted — and two independent age keys, one per machine, mean neither one alone has to be shared with the other.
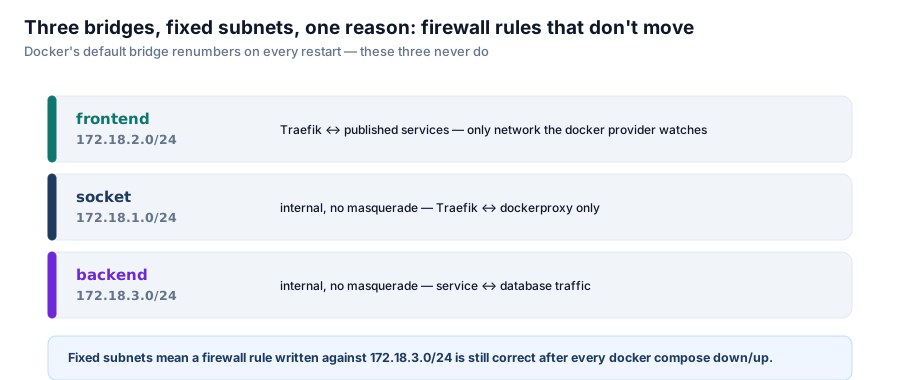
docker Three Docker Networks, Fixed Subnets, One Reason: Firewall Rules That Don't Move frontend, socket, and backend are declared with fixed CIDR blocks on vmi2633427 for a reason that has nothing to do with routing and everything to do with what a firewall rule can trust.
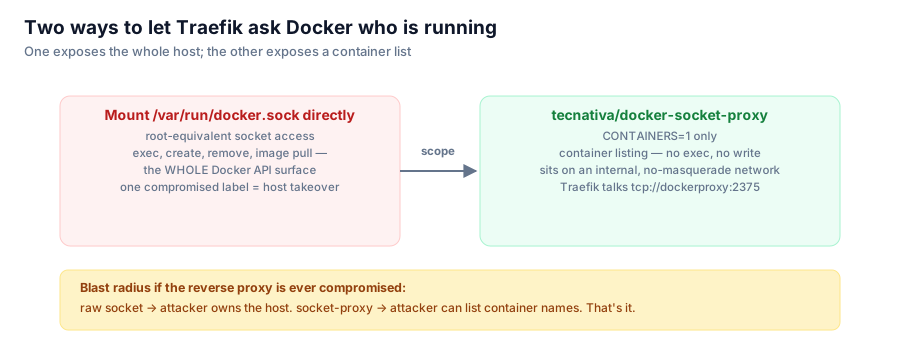
docker Don't Give Your Reverse Proxy Root on the Host Traefik needs to know which containers exist and what labels they carry — it does not need exec, write, or image management. tecnativa/docker-socket-proxy is the difference between those two things.
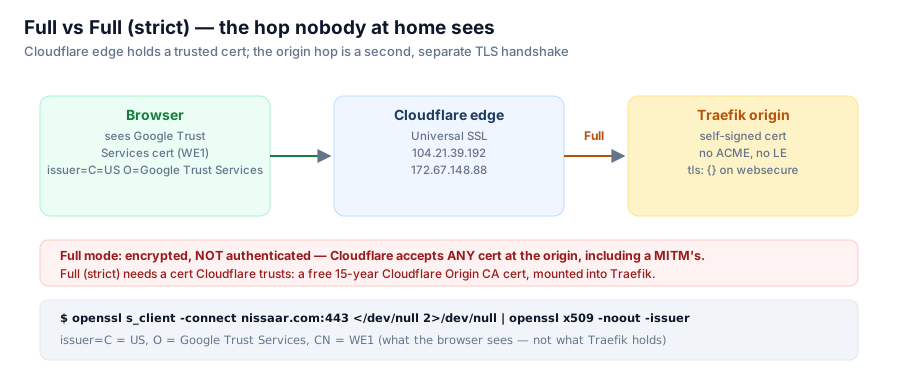
traefik The TLS Handshake Nobody at Home Sees: Full vs Full-Strict Behind Cloudflare Traefik on vmi2633427 issues no certificates and holds no ACME credentials — the browser's cert and the origin's cert are two entirely different documents, and closing the gap between them is one flag in Cloudflare's dashboard.