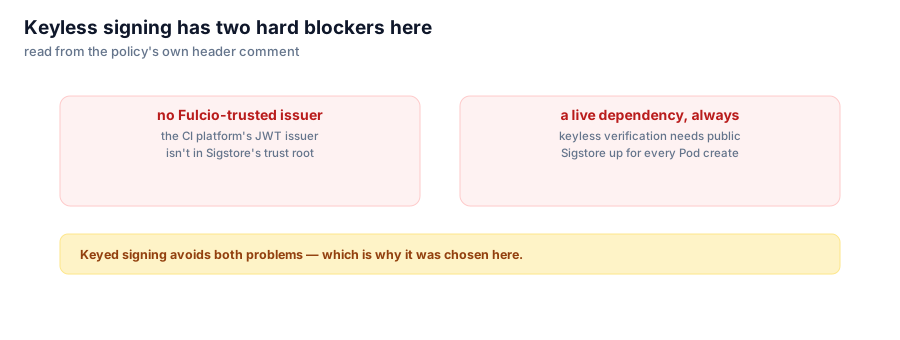
cosign Keyless Signing Has Two Hard Blockers Here Cosign's keyless mode needs a CI platform Fulcio trusts and a live path to public Sigstore at admission time. This cluster fails one of those for one CI platform, and fails the other for both — so the phase-in policy ships key-based only.
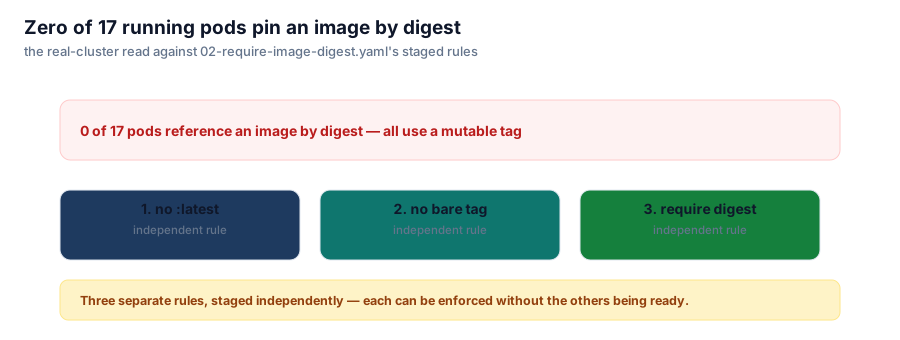
kyverno Zero of 17 Pods Pin a Digest A read-only Kyverno run against the real Pods in a namespace found 17 Pods and zero pinning an image by digest. That number is why the digest policy ships as three separate rules instead of one.
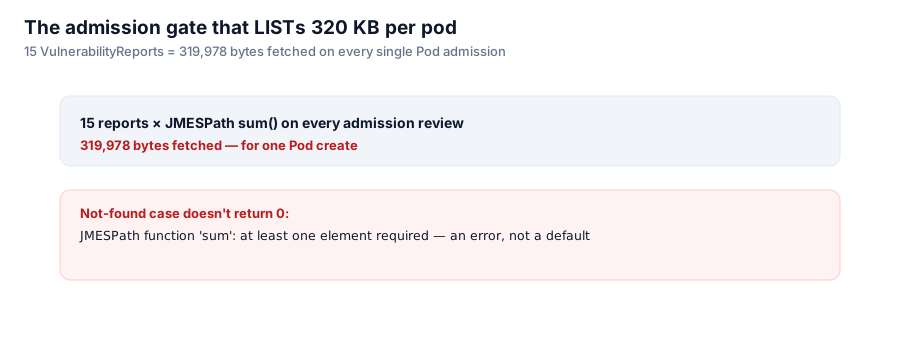
kyverno The Admission Gate That Lists 320 KB Per Pod A Kyverno policy that blocks Pods on CRITICAL CVE counts has to LIST every VulnerabilityReport in the namespace on every admission — 319,978 bytes for 15 reports. And the unscanned case, which should return zero, errors instead.
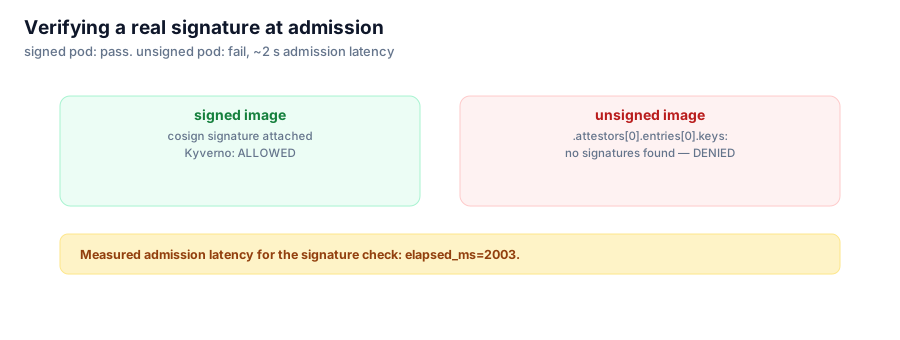
cosign Verifying a Real Signature at Admission Two Pods, one signed and one not, evaluated against a Kyverno verifyImages policy holding a real public key. The signed Pod passes; the unsigned one fails with 'no signatures found' — and the whole run takes about two seconds.
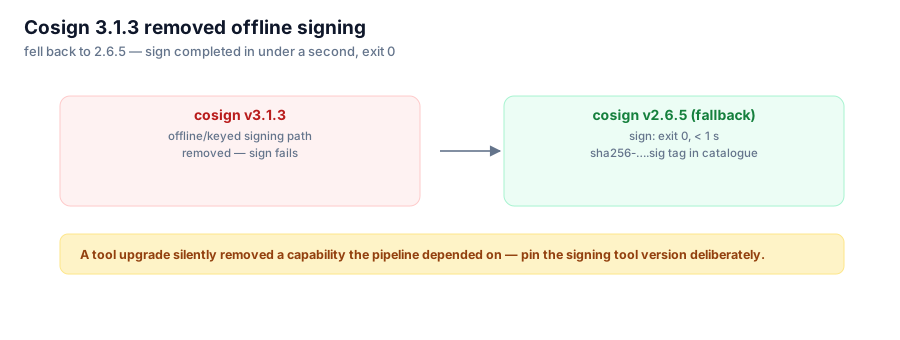
cosign Cosign 3.1.3 Removed Offline Signing cosign v3.1.3 refuses --tlog-upload=false with --signing-config, which blocks signing on a host with no public Sigstore egress. The fallback to v2.6.5 signs in under a second and puts a .sig tag straight into the registry catalogue.
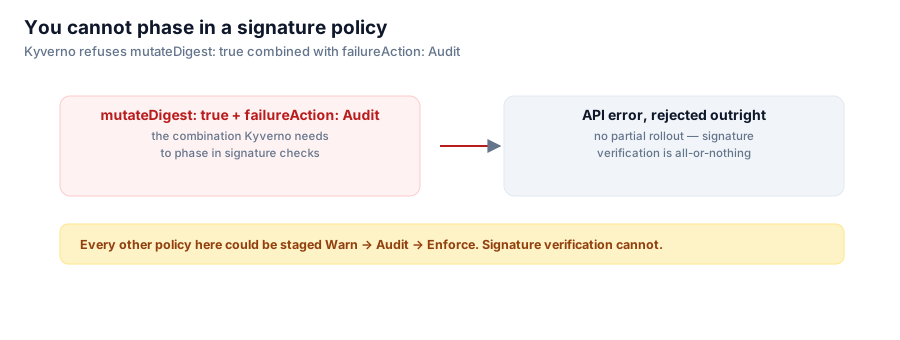
cosign You Cannot Phase In a Signature Policy Every other Kyverno policy can be trialled in Audit mode first. Image-signature verification cannot — Kyverno 1.17.2 refuses mutateDigest:true together with failureAction:Audit, and rejects the policy outright.