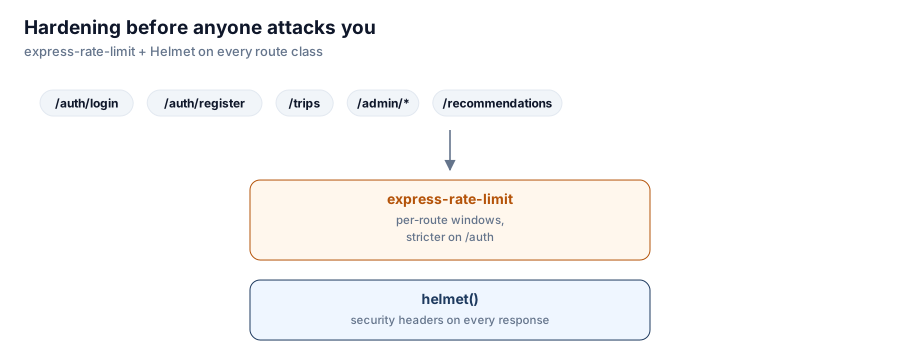
security Rate Limiting an API Nobody Is Attacking Yet express-rate-limit and Helmet went into Fishing Tracker Pro's backend before there was any evidence of abuse — because CodeQL found six unrated routes before an attacker did.
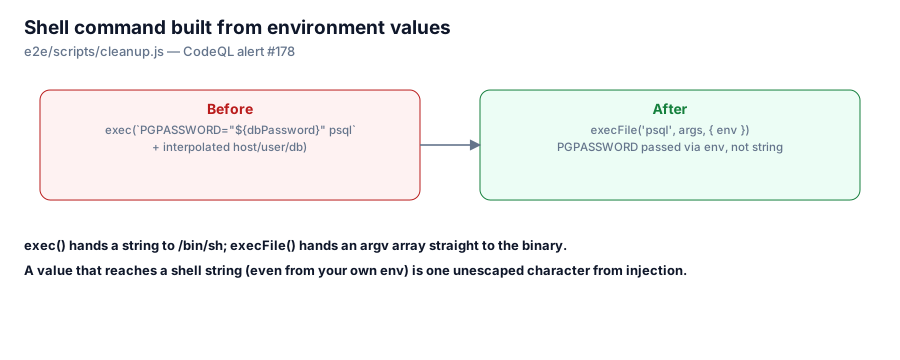
security The CodeQL Alert: Shell Command Built From Environment Values Alert #178 flagged a cleanup script that built a shell string from process.env.DB_PASSWORD. The fix isn't escaping the value — it's not building a shell string at all.