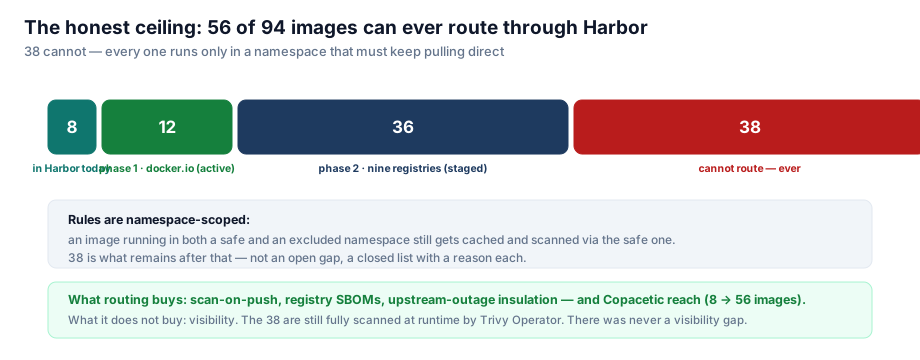
supply-chain The Honest Ceiling: Why 38 of 94 Images Can Never Route Through Harbor Maximum Harbor routing is 56 of 94 images — the other 38 run only in namespaces that must keep pulling direct, each one a dependency loop with a written reason. The honest framing: routing raises patchability, not visibility.
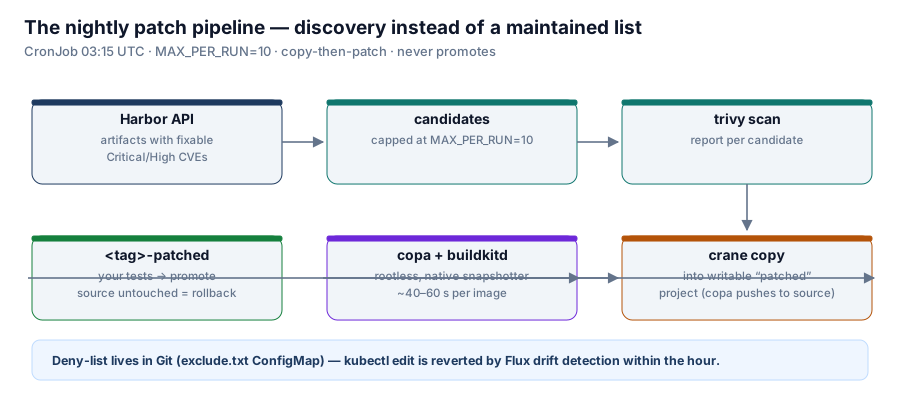
containers Patching Without a List: A Nightly Pipeline That Finds Its Own Targets Every image list you maintain by hand is stale the day after you write it. Our Copacetic pipeline discovers candidates from Harbor's own scan results instead.
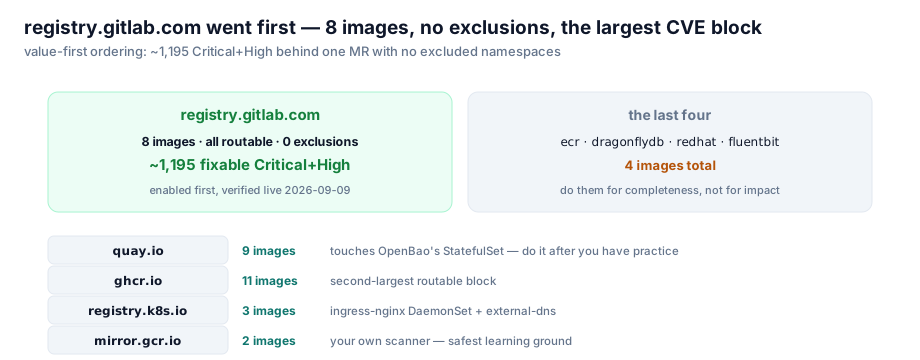
supply-chain Why registry.gitlab.com Went First: Eight Images, No Exclusions, the Largest CVE Block Queue order for routing registries through Harbor was chosen by value, not size: gitlabcom carries 8 images, zero excluded namespaces, and roughly 1,195 fixable Critical+High findings — the single largest CVE block in the estate.
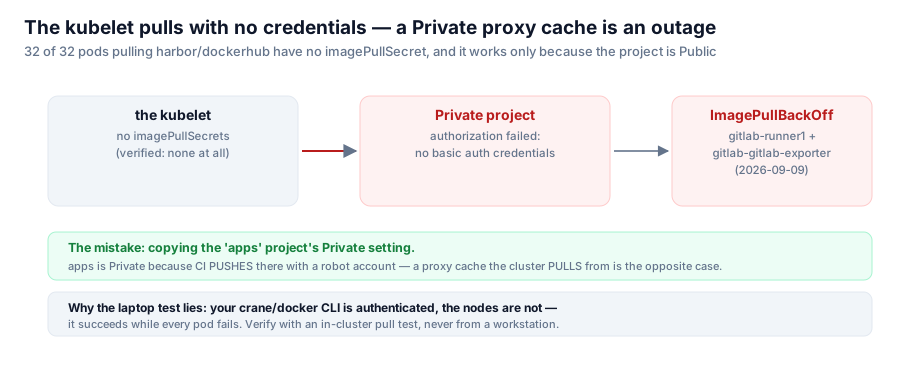
kubernetes Public Project or Nothing: The Proxy-Cache Setting That Is Not a Preference The kubelet pulls with no imagePullSecrets at all — 32 of 32 pods pull from harbor/dockerhub and it works only because the project is Public. Copying the 'apps' project's Private setting took two workloads down.
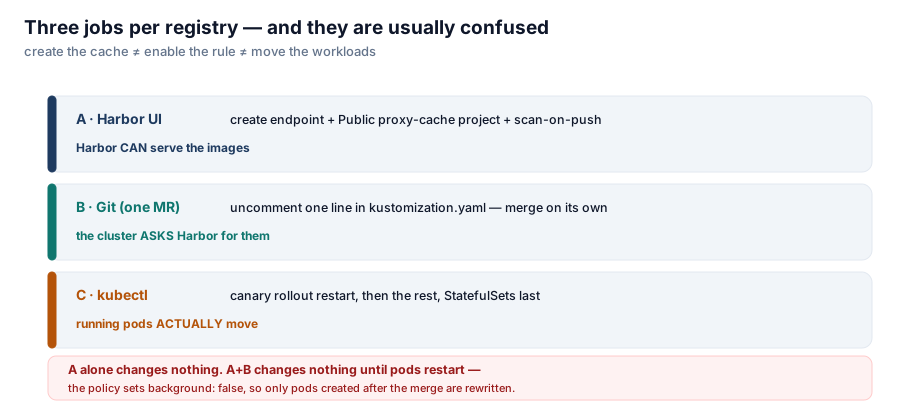
platform-engineering The Registry Routing Campaign: Two of Nine, and Why It Goes One at a Time Routing upstream registries through Harbor is three separate jobs per registry — create the cache, enable the rule, move the workloads — and the campaign only works done one registry at a time, safest first.