cosign Keyless Signing Has Two Hard Blockers Here Cosign's keyless mode needs a CI platform Fulcio trusts and a live path to public Sigstore at admission time. This cluster fails one of those for one CI platform, and fails the other for both — so the phase-in policy ships key-based only.
pod-security-admission Four of Our Six Policies Shouldn't Be Policies A Kyverno ClusterPolicy with four rules — non-root, no privileged, no privilege escalation, drop ALL capabilities — is four rules Pod Security Admission already enforces for free. The policy file says so in its own header.
trivy Nine Compliance Specs Hidden in the Binary Trivy 0.73.0 ships nine compliance specs compiled into the binary — CIS for AWS, Docker, EKS, Kubernetes and RKE2, plus NSA and both Pod Security Standards profiles. Nothing in the help output tells you their names.
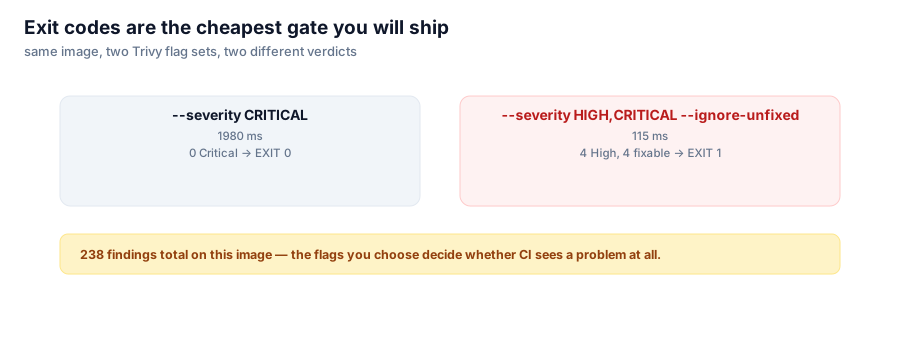
trivy Exit Codes Are the Cheapest Gate You Will Ship One flag decides whether a Trivy scan blocks a pipeline. On the same image, --severity CRITICAL exits 0 and HIGH,CRITICAL --ignore-unfixed exits 1 — and the gate that actually fires is the one that costs 115 milliseconds.
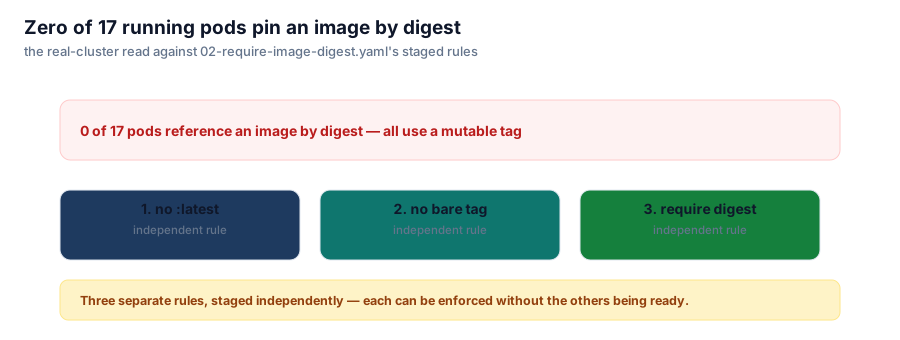
kyverno Zero of 17 Pods Pin a Digest A read-only Kyverno run against the real Pods in a namespace found 17 Pods and zero pinning an image by digest. That number is why the digest policy ships as three separate rules instead of one.
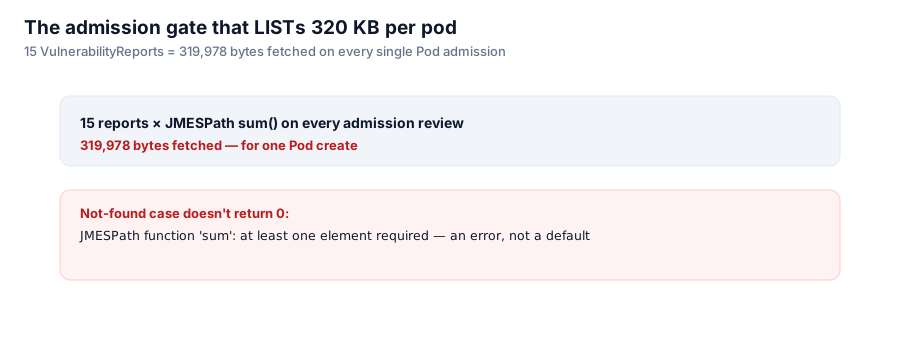
kyverno The Admission Gate That Lists 320 KB Per Pod A Kyverno policy that blocks Pods on CRITICAL CVE counts has to LIST every VulnerabilityReport in the namespace on every admission — 319,978 bytes for 15 reports. And the unscanned case, which should return zero, errors instead.
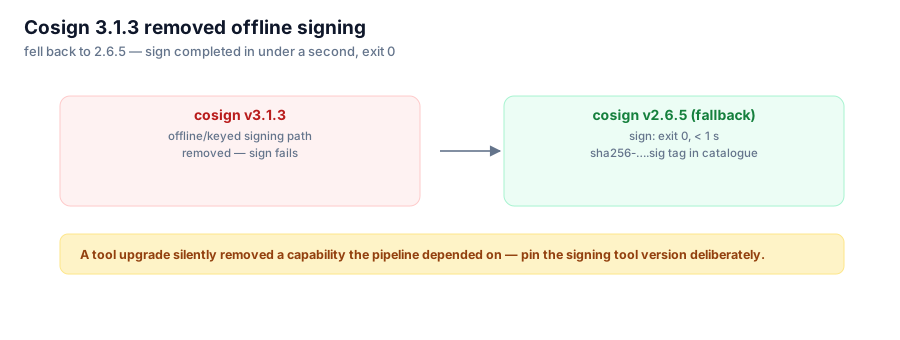
cosign Cosign 3.1.3 Removed Offline Signing cosign v3.1.3 refuses --tlog-upload=false with --signing-config, which blocks signing on a host with no public Sigstore egress. The fallback to v2.6.5 signs in under a second and puts a .sig tag straight into the registry catalogue.
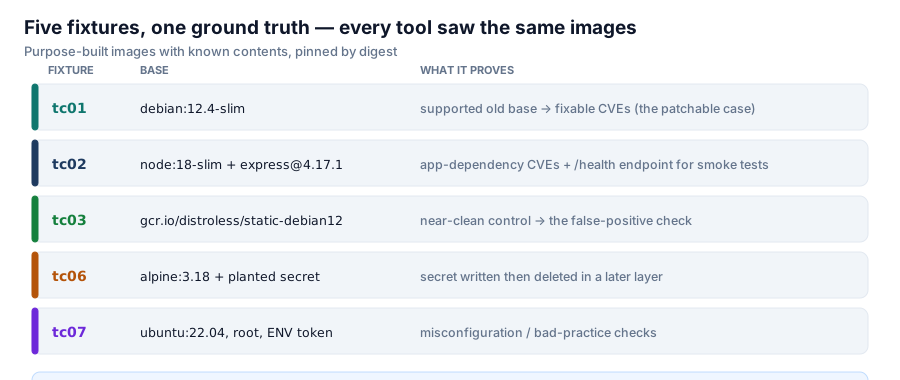
containers Build the Fixtures Before the Tools: A Testing Methodology for Container Scanners A scanner comparison against whatever happens to be running is a number, not a comparison. Here is the fixture set — known-bad images pinned by digest — that makes tool claims testable.
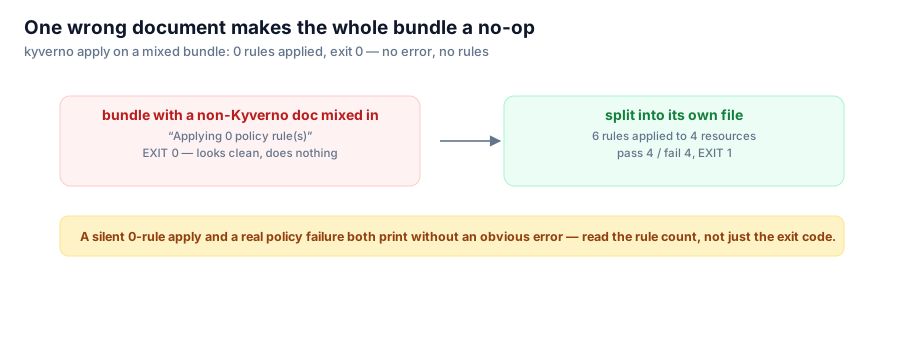
kyverno A Policy Bundle With One Wrong Document Is a Silent No-Op A policy file carrying its companion ClusterRole made `kyverno apply` report 'Applying 0 policy rule(s)' and exit 0 — a green CI gate enforcing nothing. The fix is to assert the rule count, not the exit code.