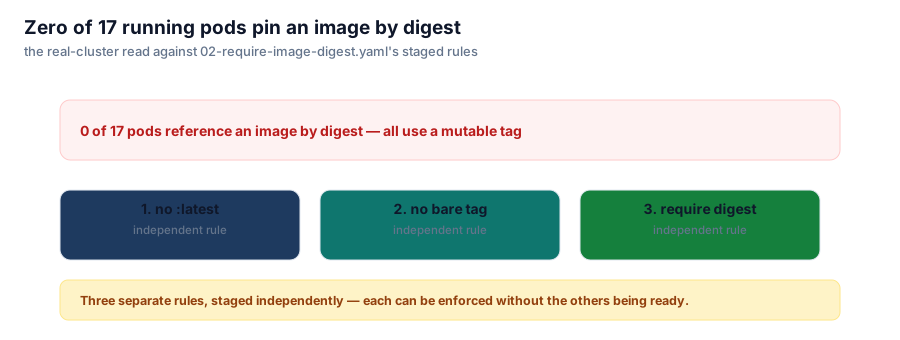
kyverno Zero of 17 Pods Pin a Digest A read-only Kyverno run against the real Pods in a namespace found 17 Pods and zero pinning an image by digest. That number is why the digest policy ships as three separate rules instead of one.
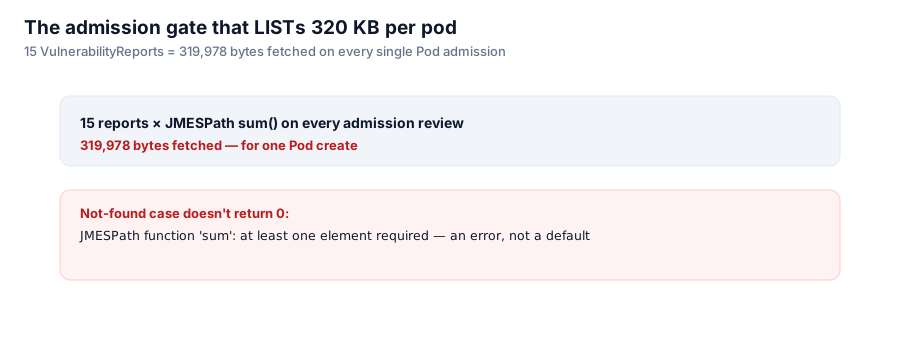
kyverno The Admission Gate That Lists 320 KB Per Pod A Kyverno policy that blocks Pods on CRITICAL CVE counts has to LIST every VulnerabilityReport in the namespace on every admission — 319,978 bytes for 15 reports. And the unscanned case, which should return zero, errors instead.
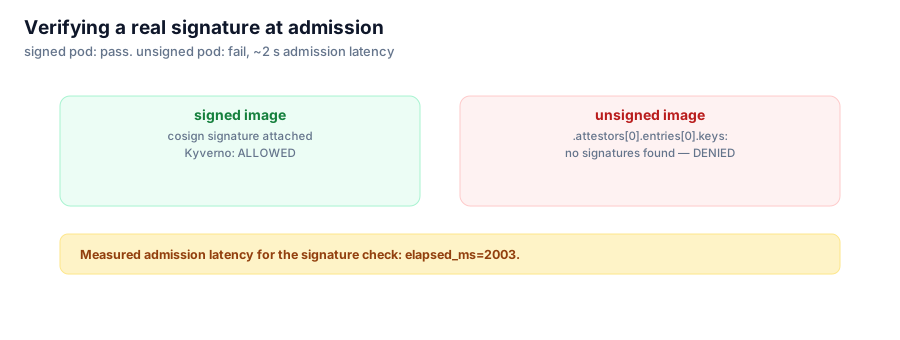
cosign Verifying a Real Signature at Admission Two Pods, one signed and one not, evaluated against a Kyverno verifyImages policy holding a real public key. The signed Pod passes; the unsigned one fails with 'no signatures found' — and the whole run takes about two seconds.
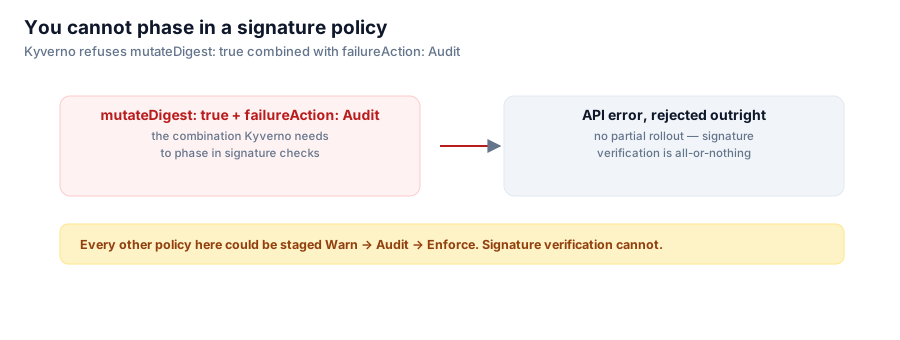
cosign You Cannot Phase In a Signature Policy Every other Kyverno policy can be trialled in Audit mode first. Image-signature verification cannot — Kyverno 1.17.2 refuses mutateDigest:true together with failureAction:Audit, and rejects the policy outright.
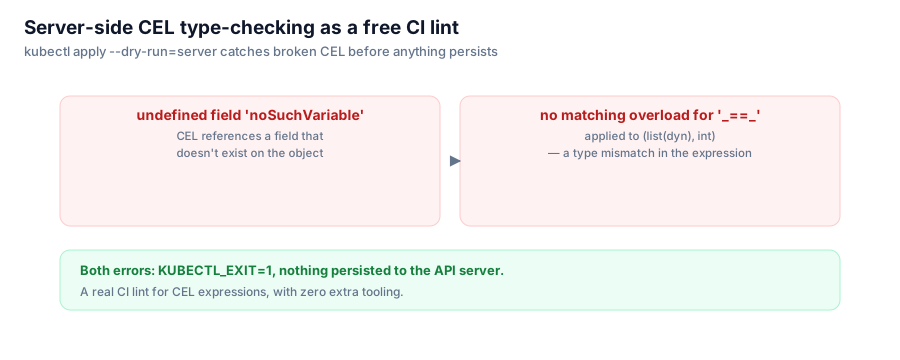
cel Server-Side CEL Type-Checking as a CI Lint kubectl --dry-run=client accepts a ValidatingAdmissionPolicy with a broken CEL expression. --dry-run=server compiles it, names the column of the error, and exits 1 — with nothing persisted. That is a free CI lint.
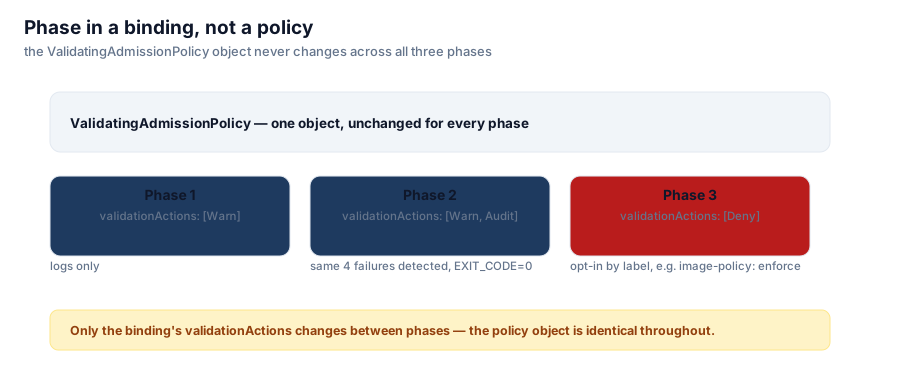
vap Phase In a Binding, Not a Policy With native VAP, the grace period lives in the binding's validationActions, never in the policy object. The same four violating Pods still report as failures under [Warn, Audit] — but the run exits 0, and phase 3 is opt-in by namespace label.
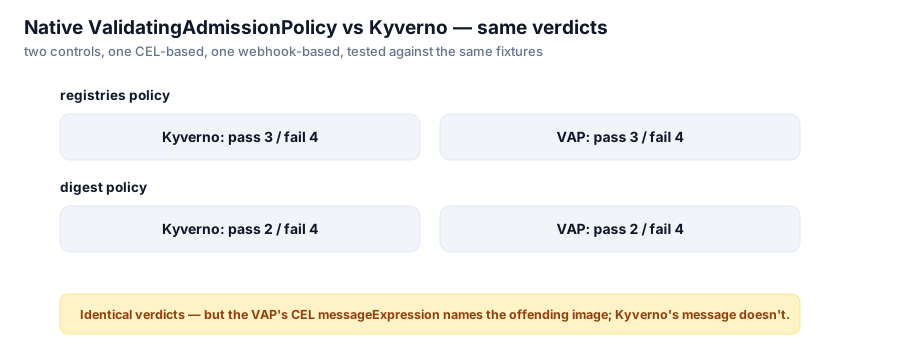
vap Native ValidatingAdmissionPolicy vs Kyverno, Same Two Controls The registry allow-list and the digest-pinning control were reimplemented as native CEL ValidatingAdmissionPolicies and run against the identical fixtures. Same verdict on every Pod — and CEL's messageExpression names the offending image.
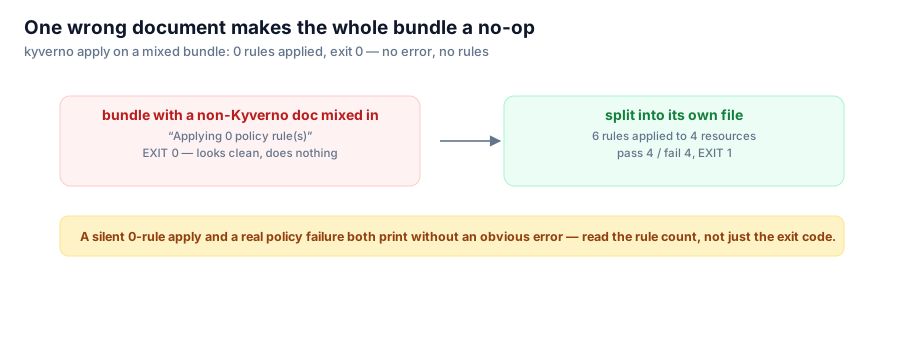
kyverno A Policy Bundle With One Wrong Document Is a Silent No-Op A policy file carrying its companion ClusterRole made `kyverno apply` report 'Applying 0 policy rule(s)' and exit 0 — a green CI gate enforcing nothing. The fix is to assert the rule count, not the exit code.
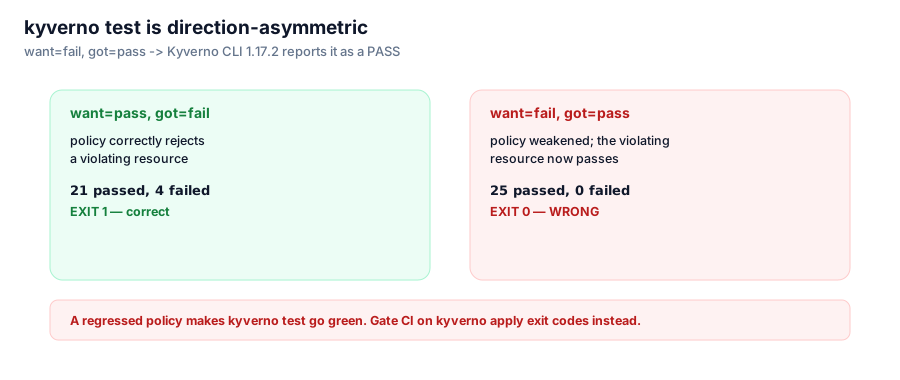
kyverno Kyverno Test Goes Green When You Weaken a Policy A negative control on `kyverno test` found it is direction-asymmetric: assert `result: fail` on a resource the policy now lets through, and it prints 'Want fail, got pass' — then reports 25 tests passed and exits 0.